
Beyond Your Walls: Why Vendor Security Is Your Security
Date: November 17 Time: 12:00 pm - 1:30 pm
Cost: This event is being offered as a free education session.
Woburn, MA 01801

Access to confidential, sensitive, and personal data should be limited to vendors with a genuine need for it, and the decision to provide access should be backed by real due diligence, not just a signed contract. Threat actors increasingly target the supply chain rather than attacking companies head-on, making vendor security an external vulnerability that many leaders underweigh. In addition, vendors increasingly pose regulatory risk related to privacy and AI practices.
This session covers practical, high-stakes topics: what contract language actually protects you, how to vet vendor security, privacy, and AI practices before entering into an agreement, and concentration risk where several “independent” vendors turn out to share a single point of failure (e.g., the same cloud provider), so one outage or breach cascades across all of them. The core principle: outsourcing doesn’t outsource responsibility. For example, hiring a third-party IT provider or storage vendor doesn’t relieve a company of its data management obligations, and compliance doesn’t end once your own house is in order.
Due diligence and sound contractual protections with every vendor are part of the company’s responsibility. Never blindly trust a vendor.
Presenters
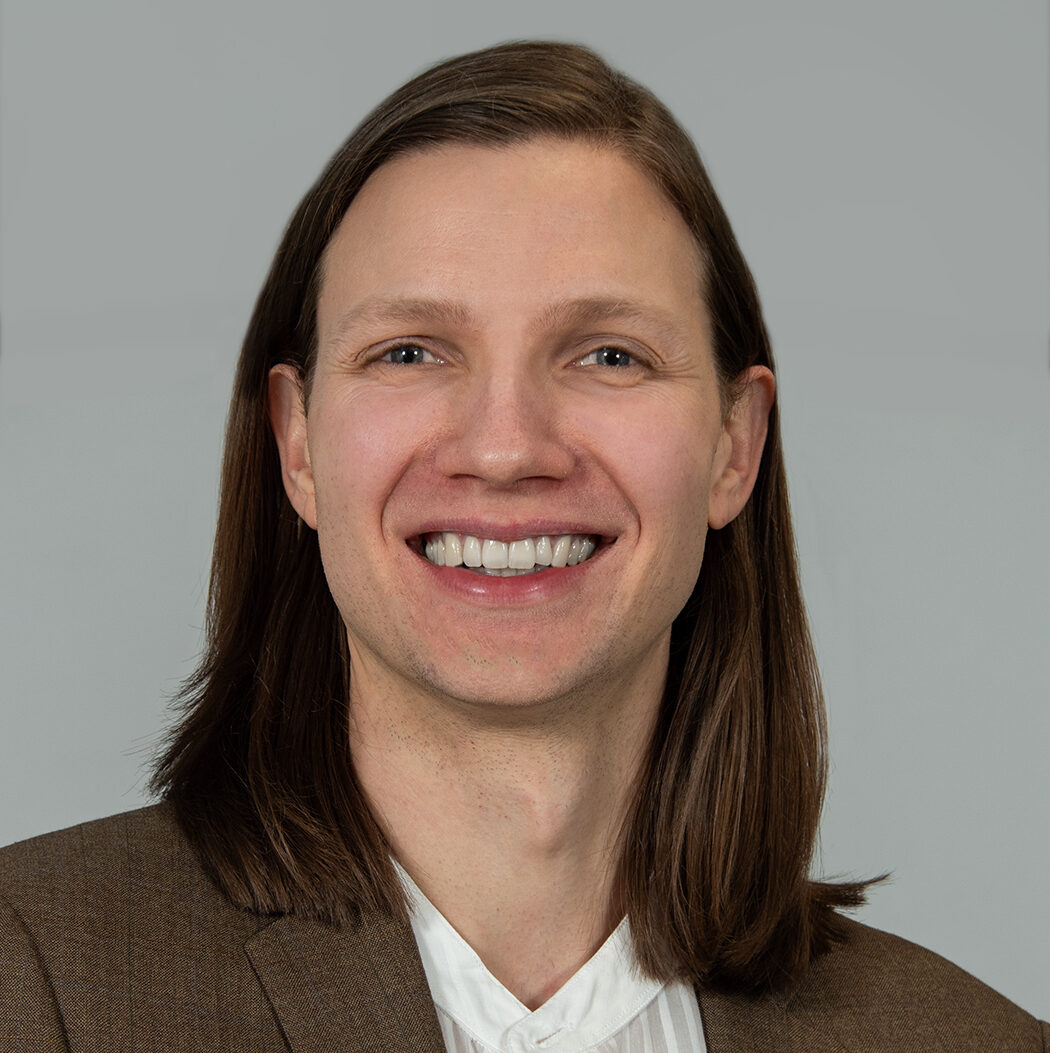
Alex is counsel in the firm’s Cybersecurity and Privacy group. He has spent the last decade advising clients on a broad spectrum of cybersecurity, data management, and privacy issues. His experience includes overseeing response to cybersecurity and privacy incidents, managing privacy and cybersecurity audits, assessments, and certification processes, drafting written information security policies and privacy policies, implementing incident response programs, reviewing contractual language with privacy, cybersecurity, and data handling implications, creating privacy compliance programs from the ground up, and advising on the impact of privacy and cybersecurity concerns in mergers, acquisitions, and venture financings.
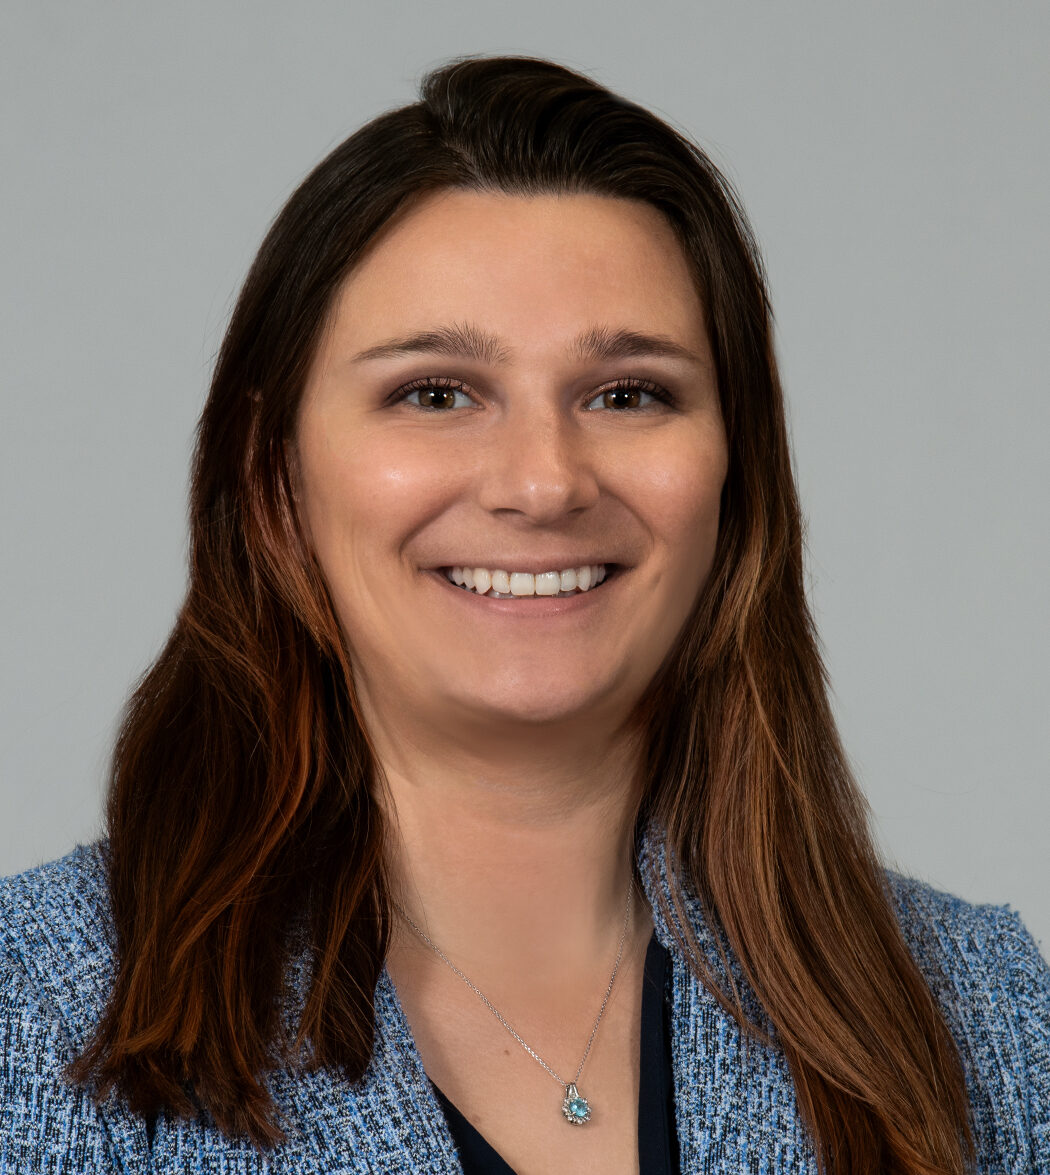
Katarina focuses her practice on cybersecurity and data privacy matters and intellectual property. In the dynamic field of cybersecurity and data privacy, Katarina counsels clients on cybersecurity and data privacy compliance and litigation stemming from an organization’s data management and governance practices, helping them navigate complex U.S. federal and state regulations as well as international requirements like the GDPR, PIPEDA, and global data transfer frameworks. In the complex area of intellectual property, Katarina has extensive patent preparation and prosecution experience in a variety of technical fields, including aerospace and defense, automation and robotics, autonomous vehicle, and consumer products.

As a cybersecurity and privacy attorney, Muhammad regularly assists client’s in drafting and negotiating a wide range of agreements, including data processing agreements, business associate agreements, software-as-a-service (SaaS) agreements, and data license agreements. His practice includes developing and implementing comprehensive information security policies, privacy policies, AI usage policies, and terms of use agreements. Usman also conducts in-depth privacy and cybersecurity risk assessments, including Data Protection Impact Assessments (DPIAs). He has addressed privacy concerns in mergers and acquisitions (M&A) and provides counsel on a broad array of privacy and cybersecurity matters across national, international, and industry-specific frameworks.